Enterprise controls without enterprise weight.
Role-based access control, configurable approval workflows, immutable audit trail, and compliance-ready records — the platform controls that let growing businesses operate with the rigor of enterprise-scale operations, without the enterprise complexity or cost.
 ⤢
What Platform Controls handles.
Access, approvals, audit, and authentication — the controls every action on the platform passes through.
How platform controls run.
These are the control operations that run behind everything else — user setup, approval enforcement, and audit trail retrieval when someone asks.
User Setup and Role Assignment
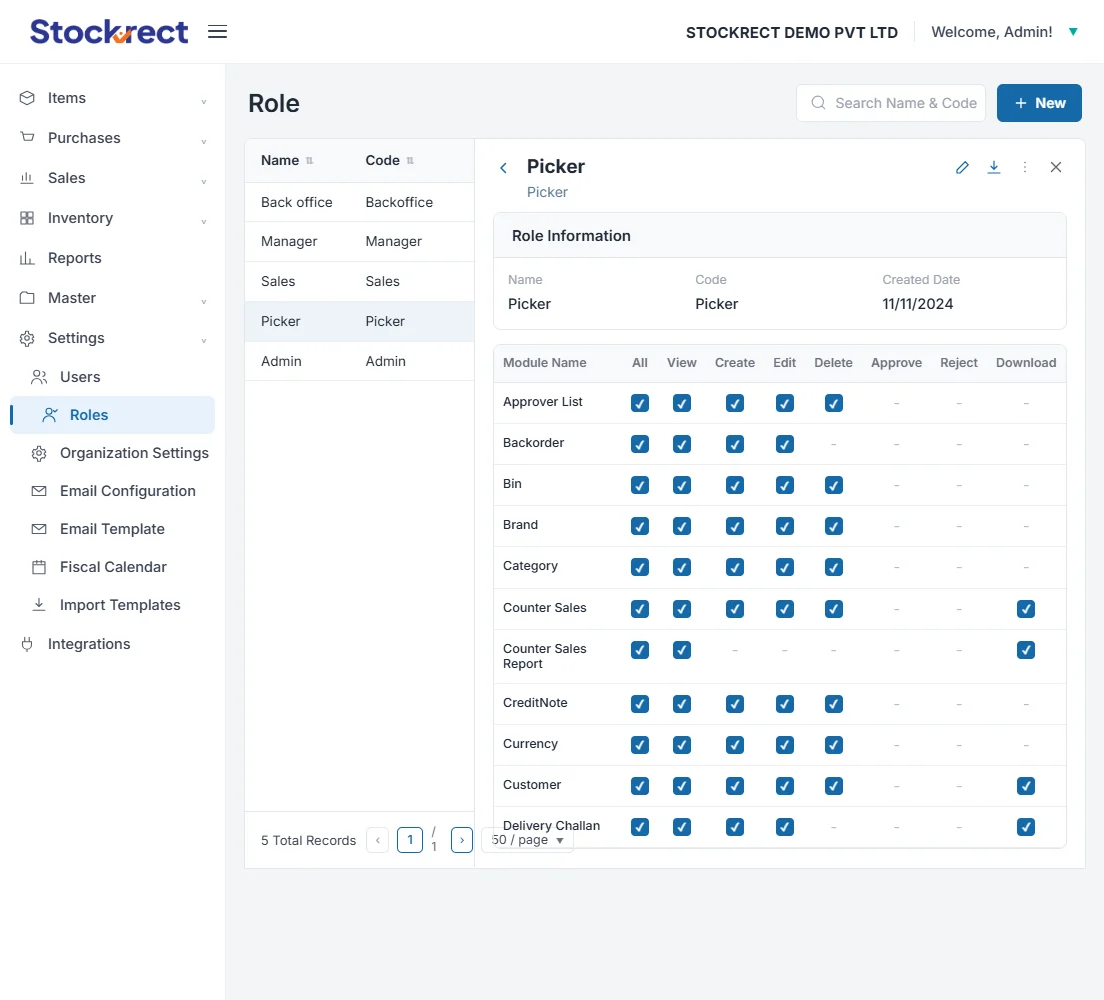
Admin creates a new user, assigns to a role (Sales, Warehouse, Finance, Management, etc.). Role determines what modules, actions, and data the user can access. Custom roles can be created for specific responsibility patterns. New user is productive within minutes, restricted to only what they need.
Approval Workflow Enforcement
High-impact actions (stock adjustment beyond threshold, customer credit override, vendor payment above amount) route through configured approval chains. Approvers see full context and can act from mobile or desktop. Rejected requests return with reason. Complete audit trail preserved.
Audit Trail for Compliance
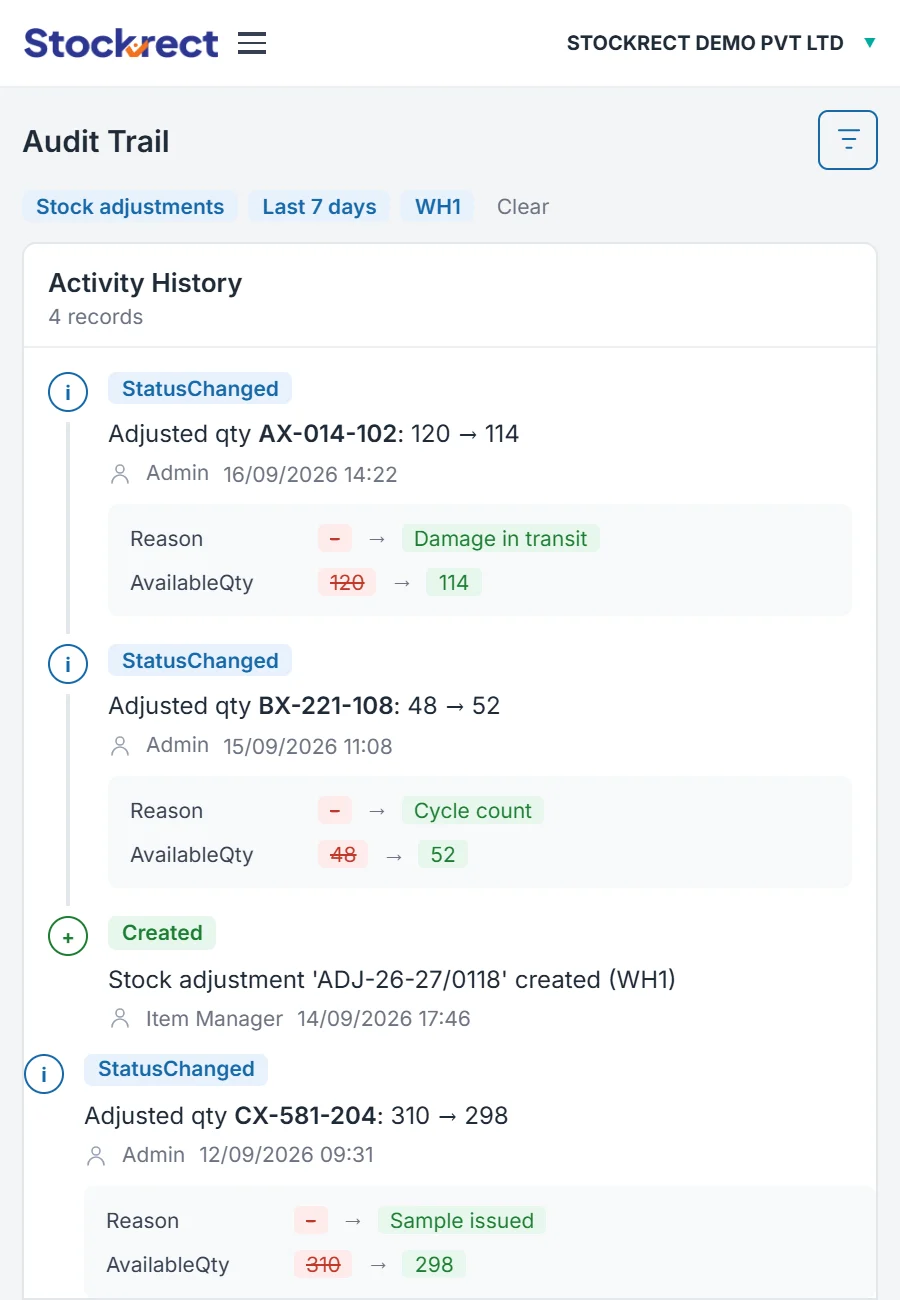
Every action captured with user attribution, timestamp, IP address, and change details. Audit trail is immutable — records cannot be modified after creation. When auditors ask, one query returns complete history. When incidents occur, root cause analysis is straightforward.
Who uses Platform Controls.
Admins configure it, management and compliance review it, and every other user operates inside it whether they notice or not.
How Platform Controls connect.
Controls aren't a module you visit — every action on the platform passes through the permission structure and lands in the audit trail.
Common questions about platform controls.
Very granular. Access can be restricted at module level (Sales, Procurement, Warehouse), function level (view vs edit vs delete), and data level (specific warehouses, customer groups, product categories).
Every action creates an audit record with user, timestamp, IP address, and change details. Records are immutable — cannot be modified after creation. Retention configurable per compliance requirements.
Yes. Approval chains configurable by amount, category, or user role. Multi-level approvals supported. Approvers can act from mobile or desktop.
Configurable. Recommended for administrative accounts and high-privilege users. Supported: TOTP (Google Authenticator, Authy), SMS-based OTP, email-based OTP.
The audit trail, access controls, and record retention support customer compliance with data protection regulations. Currently designed with DPDP Act requirements in mind for Indian operations; extensible to GDPR and other frameworks.
Enterprise controls, growth-paced.
A 30-minute discovery call showing how platform controls give you compliance-ready operations. If it's a fit, we'll follow up with a tailored proposal.
Have questions first? Email hello@stockrect.com